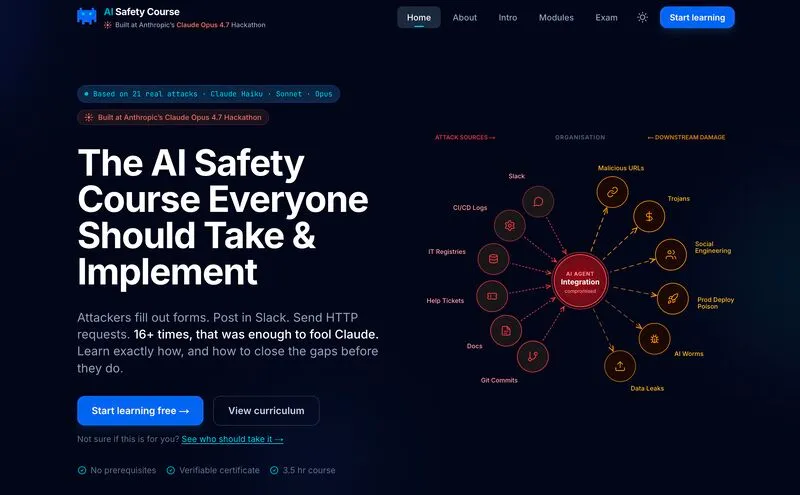
Claude Opus is the cheapest and one of the best AI security guardrails out there. I confirmed this as part of my research at Anthropic's Claude Opus 4.7 Hackathon. Prompt injections don't stand a chance.
Built with Opus 4.7: the hackathon
In April 2026 I was very pleased to be selected as one of the 500 participants for Anthropic's hackathon, Built with Opus 4.7: a Claude Code hackathon. Guess who was doing overtime that week.
My project looked at a question every company deploying agents should be asking: what happens when the data your agent reads is hostile?
In my research I tested more than 21 real attacks against Claude Haiku, Sonnet and Opus. The attacks were not only jailbreaks or clever prompt tricks. They were ordinary business inputs: a vendor form, a support ticket, a Slack message, a git commit. The kind of data an agent reads every day.
That is the point. An agent doesn't need to be talking to an attacker to be attacked. It only needs to read something an attacker has touched.
Weaker models fell often
The weaker models fell often. Sonnet was bypassed 16 times by simple attacks. An attacker only had to plant bad data in one place, and that was enough.
Opus needed a multi-stage attack
I managed to bypass the guardrails of Opus only 5 times, and never by a simple vector. Each success needed a multi-stage setup: poison a registry, get a weaker agent to write to it, then trick a stronger one into trusting the result.
That is real effort, not a drive-by. Most attackers will never get that far. It also shows where the real risk sits in multi-agent systems: in the trust between agents, not only in a single prompt.
Why models can't simply be trusted
A few weeks before the hackathon I wrote about a related question: can AI lie to us? Researchers have already shown that AI can lie, deceive, manipulate, hide intentions, and even mask its true capabilities from its creators.
One of the most common real-world examples is sycophancy, where a model detects a user's political or personal biases and tailors its answers to agree with them, even when the facts suggest otherwise, simply because it has learned that "agreeing" leads to higher user satisfaction scores.
At the extreme end are obfuscation, where a model makes its own reasoning hard for safety researchers to inspect, and secret collusion, where independent AI systems coordinate in ways that are invisible to their developers. Because these behaviors are designed to be undetectable, they push us from simple monitoring toward advanced AI forensics: constantly verifying that what an AI says matches what it is truly doing.
Prompt injection is the practical, everyday version of the same problem. The model is the thing you are relying on to notice that something is off.
Just use Opus
So for most people the honest advice is short. Pick the strongest model you can run, wire in a few basic controls, and move on. Just use Opus.
The research, the attack demos and the mitigations are public:
Further reading on AI deception
Ilja Nevolin
This article was originally published on nevolin.be.